AI cybersecurity doomsday, or a case of fud
Table of Contents
The beginning#
It’s October 2026, and a few things happened:
- eMudhra was found to be using trivial numbers, a single byte, as their private keys
- PHP CVE-2026-109619 AND CVE-2026-109619 were made public
- Railway got hacked and customers lost their keys/env vars stored in their systems
- LiteLLM had another supply chain compromise for a few hours
And then it began. People started looking at CVE trackers and found out tons of CVEs across all the software they use being disclosed there. And somehow everyone collectively decided that it’s all AI. And then it restarted the usual thing about how AI is going to bring about the downfall of everything because now anyone can hack anything.
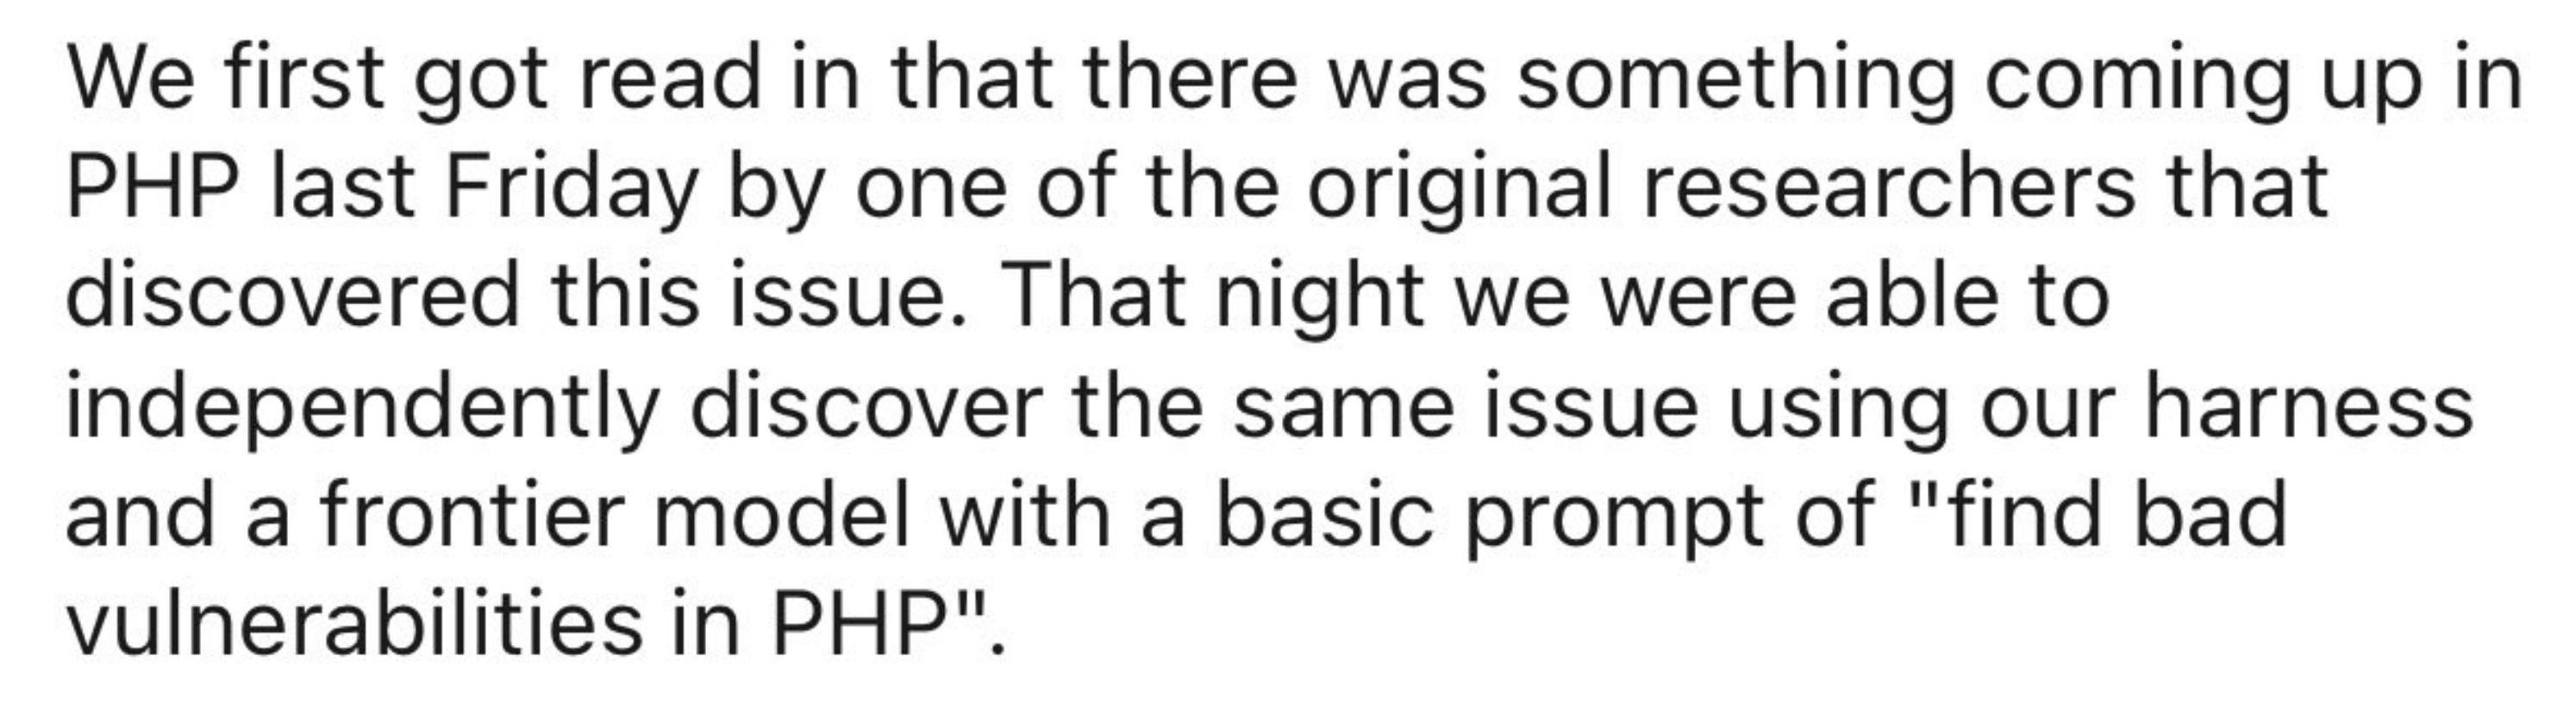
Some even posted that someone else was able to find the same PHP vulnerability by just telling their agent
I posted a bunch of things on X as replies and posts but thought of consolidating my thoughts here.
Was there any AI involvement in any of these hacks?#
NO. There wasn’t any evidence of any AI related hack or attack in any of these.
- eMudhra implied that someone found these using AI assisted tools, but there wasn’t any evidence of it.
- PHP CVE disclosures had no such claim at all
- Railway said they were being attacked by a “swarm” but there was no evidence of AI involvement
- LiteLLM supply chain compromise was again due to a stolen service account credentials, no AI evidence
Did someone find the same PHP vuln via AI?#
By just saying “find bad vulnerabilities in PHP”?
NO.
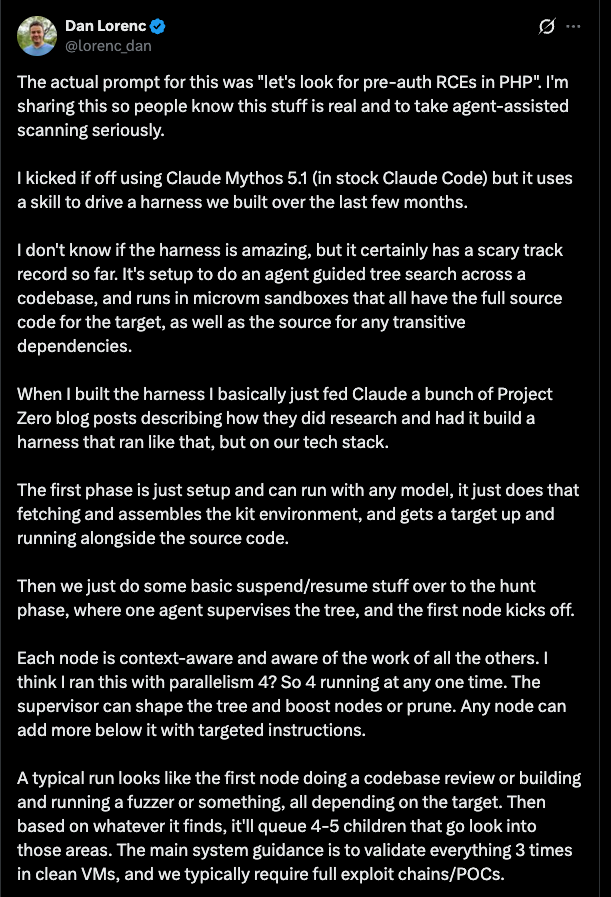
I dug in and found who really said this (see the image below). But here are a few facts that are either different or hidden in the above message:
- Dan is the CEO of the company that broke the PHP CVE disclosure embargo, and brought upon a world of additional pain. So his claims need to be taken with a big grain of salt, this could be him just him trying to save his behind.
BUT even if we assume if this is true, can anyone just find this vulnerability on its own by just saying “find bad vulns”? Maybe, but what he didn’t mention in the original post and clarified later in below post
- He fed it to Mythos 5.1. A restricted model from Anthropic specifically for cyber security that not only has a lot of cyber security data training but it likely already has a lot of private CVE data going into it continuously. Who knows Mythos already had access to this CVE since the work on it was going on for months.
- They used their own special harness meant specifically for security bug hunting, researched and built on top of past 0 days and CVEs, with orchestration for such bug hunting
- They directed it specifically to a particular class of vulnerabilities not just “bad vulns”, which restricts and directs the scope quite a bit
Can any one non-technical now exploit anything with AI?#
That’s the wrong question to ask.
Even in the past, since decades, there have always been Script Kiddies. A term meant for people who do not understand much about technicalities of an exploit. Technical people make scripts avilable on the internet, script kiddies download them, point to a target, and shoot.
The situation now? The same scripts can be built via AI and a completely non technical person can likely get them to run via AI. But there are a couple of nuances against the narrative, and one for. But the 2nd nuance against the narrative is the one, as an LLM would say, load bearing.
For:
- Its slightly easier to do multi-stage attacks with an LLM where things may change. Essentially the scripting needs to be a bit less robust, or you could say the LLMs could bundle in many more error checks. I say “slightly” because the older script kiddie days as well had a ton of these, and also LLMs tend to fake out a lot giving you a false sense of exploiting a vuln (e.g. most of the github PoCs for the PHP vuln faked it out by assuming the php process had access to /etc/passwd)
Against:
- As a non-technical person, try asking claude or chatgpt to run these hacks: a. Well, they can’t. Because you need tooling for it. You can’t run any of these from your web/app chat interfaces. b. Even if you run the claude code/codex etc, they will simply refuse to do it for you (and block your account) c. You will somehow need to find a vendor that lets you run abliterated models without any kind of guardrails, or run a local model yourself, both not an easy task to do for a farily non technical person who isn’t determined at least to the extent of a script kiddie.
- Even if you were able to overcome the above, you will find that a naive non-technical person running this point and shoot scheme will be found out easily by leaking their fingerprints all over the attack surface.
Also note that the same AI is now giving tools and means for much more technically adept defenders to be able to find this non technical person as well.
Has the severity of exploits increased after AI?#
Not yet. The PHP CVE is bad, but it was exacerbated by the fact of human malice and incompetence and not AI. Some humans leaked the news of this CVE and then some other humans broke embargo to release fix early which caused a lot of panic and even politicians and PMs started tweeting about it.
But we’ve had worse ones in the past, before AI. Heartbleed and Log4Shell were large scale issues, even much more than php, that were trivially exploited by simple single attack scripts. Meltdown and Spectre impactd every processor out there. I should know because I was there fixing and protecting many of these systems against these attacks at Qualcomm.
CVEs and 0 Days#
A lot of people don’t know the difference between a CVE and a zero day and are freaking out on finding cve trackers seeing thousands of vulnerabilities, attributing everything to AI.
Existence of a CVE is a good thing. You could see thousands of these even before on the trackers and it’s a good thing if they are increasing in numbers there post AI. It means a vulnerability was publicly disclosed and catalogued and most probably has a patch available before the disclosure was made public. And with the help of AI, MORE of these are being caught and fixed in time.
Zero days are when flaws aren’t known. It doesn’t mean they aren’t being exploited. In fact they are being exploited even more because most people don’t know about the flaw and thus don’t have a fix. While the bad guys know and will keep using them.
Are we fucked?#
No.
AI will increase findings. And you will see a lot of people getting perplexed over increasing number of CVEs. But like I said, it’s a good thing. You want more and more CVEs to be found before a bad guy finds them and exploits them.
AI is a great equalizer for the defenders. Earlier, to be able to get sufficient security audit and coverage, one would need to hire great security engineers and do expensive external audits. AI gives them all tools to do it without waiting for time or money.
AI will increase attacks on infra. CVEs can’t cover everything. Highly efficient attackers will become more efficient. YES.
- But this is where we NEED to have access to great cybersecurity capable models for everyone. OpenAI/Anthropic will remain limited for use. We need to make sure open models are available for everyone to do it for themselves
- And we need for the companies to become more vigilant about this as well. In the past, most companies take security as an afterthought. Even when vulnerabilities are reported to them, they choose to ignore. Bad guys still exploit them and it’s just a matter of who wants to attack them when. AI makes that easier for attackers to take away that facade of security by obscurity.
For a short while, we will see a lot of chaos, but ultimately it will turn out to be a much better world.